| ELF 64-bit LSB executable, x86-64, version 1 (SYSV) | |
| 2.3 MB · 2,433,024 bytes | |
6.006
/ 8 | |
| 1× | |
| 2026-10-18 13:34 UTC | |
| 2026-11-14 16:23 UTC |
| MD5 | 56075e7c63b3f9f612cde6187d4a7877 | |
|---|---|---|
| SHA-1 | 1bcfa979b7b9044ba5ce5c006bd26b0bdbeb8464 | |
| SHA-256 | 12389b8af28307fd09fe080fd89802b4e616ed4c961f464f95fdb4b3f0aaf185 | |
| SHA-512 | 7df68e37b3c2e7ce197f0d8736d06adf808343fe2d638bcd3e0f285968e1365c06b33157c6e5816b9fa9362e6adc262d3d2da45d3d1a38efb7e2ce980fce8b80 | |
| TLSH | T152B54B47B8A1A5E8C49AE2314E5161D6BAB0384D173063F32B90ABB51F72FD46F7B710 |
YARA 3 · 500 rule files from Ransomware.live
MITRE ATT&CK 3 · techniques suggested by the static analysis, not observed behaviour
Visual analysis · hover the charts for offsets
Entropy across the file
Shannon entropy (0–8) of 9,504-byte windows. Code and data sit around 4–6; a plateau above 7.2 means compressed or encrypted content (packed code, embedded archives, encrypted payloads). 0% of the file is above it.
File layout on disk
Each part of the file at its real size. Data after the last section (an overlay) is where droppers and installers often hide a payload.
| Part | Offset | Size | Share | Entropy |
|---|---|---|---|---|
| ELF header | 0x0 | 64 B | 0.0% |
2.15 |
| Program headers | 0x40 | 336 B | 0.0% |
1.6 |
| Section headers | 0x190 | 832 B | 0.0% |
1.41 |
| Gap | 0x4d0 | 2.8 KB | 0.1% |
0.0 |
| .text | 0x1000 | 1.3 MB | 54.0% |
6.16 |
| Gap | 0x1419f1 | 1.5 KB | 0.1% |
0.0 |
| .rodata | 0x142000 | 358.8 KB | 15.1% |
4.5 |
| Gap | 0x19bb0e | 18 B | 0.0% |
0.0 |
| .shstrtab | 0x19bb20 | 148 B | 0.0% |
4.28 |
| Gap | 0x19bbb4 | 12 B | 0.0% |
0.0 |
| .typelink | 0x19bbc0 | 2.1 KB | 0.1% |
4.26 |
| Gap | 0x19c454 | 12 B | 0.0% |
0.0 |
| .itablink | 0x19c460 | 416 B | 0.0% |
2.4 |
| .gopclntab | 0x19c600 | 607.1 KB | 25.6% |
5.49 |
| Gap | 0x234278 | 3.4 KB | 0.1% |
0.0 |
| .go.buildinfo | 0x235000 | 32 B | 0.0% |
3.62 |
| .noptrdata | 0x235020 | 82.6 KB | 3.5% |
5.58 |
| .data | 0x249a80 | 32.3 KB | 1.4% |
1.58 |
| Gap | 0x251bb0 | 1.1 KB | 0.0% |
0.0 |
Byte map
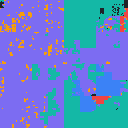
The whole file as a 128×128 picture: each pixel is 148.5 bytes, laid along a Hilbert curve so that bytes close in the file stay close in the picture and each part shows as a block. Starts top-left, ends top-right.
- Compressed / encrypted 1.2%
- Dense data 4.1%
- Code / structured data 58.9%
- Low entropy (headers, tables) 29.7%
- Text / strings 5.4%
- 0x00 padding 0.8%
Linux / ELF executable Go
Capabilities from symbols · Go function names, kept even in stripped builds
Cryptographic constants 5
Tables and constants of the algorithms compiled into the file, recognised without running or decrypting anything. A locker that brings its own cipher (ChaCha20, AES, Curve25519) needs no CryptoAPI import; many legitimate programs carry the same libraries, so this is context, not a verdict.
| Algorithm | Kind | Evidence | Confidence | Hits | First at |
|---|---|---|---|---|---|
| MD5 | hash | T constants | high | 1 | 0xe4897 |
| MD5 / SHA-1 | hash | initial values | medium | 4 | 0xe4242 |
| SHA-1 | hash | K constants | high | 28 | 0xe5a37 |
| SHA-256 | hash | K constants | high | 1 | 0x199230 |
| SHA-256 | hash | initial values | medium | 2 | 0xc8e5d |
| SHA-512 | hash | K constants | high | 1 | 0x23c8a0 |
Indicators extracted from strings · from 5,337 strings. Only those listed under Known indicators are in our database
IOC matches are re-checked against the database every time this page loads. YARA and static analysis ran once, when the file was first analysed (analyzer v6).