Known ransomware
eclipse ransomware · Windows executable (Rust) · 1 known IOC · 3 behaviour indicators · 11 ATT&CK techniques · seen 1×
- Hash matches 1 known IOC(s)
| PE32+ executable for MS Windows 5.02 (console), x86-64 (stripped to external PDB), 10 sections | |
| 2.6 MB · 2,679,296 bytes | |
6.85
/ 8 | |
| 1× | |
| 2026-10-24 09:00 UTC | |
| 2026-11-14 16:23 UTC |
| MD5 | fd126a8df5808742bb4bf46468987b11 | |
|---|---|---|
| SHA-1 | 5f9d188d6f0c9abe175c422ed1fb1a29b2610d71 | |
| SHA-256 | 17a4352c9ac6a22868dd23010f351000d8591667bb1db0504123a20393d69d06 (matched a known IOC) | |
| SHA-512 | f0e895e447db3f229f5ccfecc38969089b8f56fc75b40cbf5e77dce6a0c62c75369046510ff4564fd2be0038ba5a84d6a8233a570c0413c730d53362623457ef | |
| Imphash | f0f0d2b736cb1787d31d0c22c6f0d77b | |
| TLSH | T1E1C59D43E1E6D0E8C55AC074925B6272BA7E7C4905253EF737E4AA343EB3A403A1DB1D |
Known indicators 1
| Group | Found in | Type | Indicator | Details | TLP | Added |
|---|---|---|---|---|---|---|
|
eclipse
4 IOCs on file
|
File hash | Hash SHA256 | 17a4352c9ac6a22868dd23010f351000d8591667bb1db0504123a20393d69d06 | — | TLP:CLEAR | 2026-10-24 |
YARA · 500 rule files from Ransomware.live
No binary YARA rule matched.
Behaviour indicators 3 · from embedded strings
| Category | Indicator | ATT&CK | Evidence |
|---|---|---|---|
| Discovery | Network share discovery | T1135 | \\?\\\?\UNC\ |
| Execution | Launches a shell or LOLBin | T1059.003T1218 | cmd /c gpupdate /forceV_ cmd /c icacls " |
| Execution | WMI process creation | T1047 | try{Copy-Item $src $dest -Force -EA Stop;Invoke-WmiMethod -ComputerName $pc -Credential $cred -Class Win32_Process -Name Create -ArgumentList "C:\ProgramData\$name" -EA Stop}catch{} |
MITRE ATT&CK 11 · techniques suggested by the static analysis, not observed behaviour
Visual analysis · hover the charts for offsets
Entropy across the file
Shannon entropy (0–8) of 10,466-byte windows. Code and data sit around 4–6; a plateau above 7.2 means compressed or encrypted content (packed code, embedded archives, encrypted payloads). 29% of the file is above it.
File layout on disk
Each part of the file at its real size. Data after the last section (an overlay) is where droppers and installers often hide a payload.
| Part | Offset | Size | Share | Entropy |
|---|---|---|---|---|
| Headers | 0x0 | 1.0 KB | 0.0% |
2.41 |
| .text | 0x400 | 1.2 MB | 47.9% |
6.35 |
| .data | 0x139a00 | 3.0 KB | 0.1% |
0.3 |
| .rdata | 0x13a600 | 1.3 MB | 49.3% |
6.95 |
| .pdata | 0x27d200 | 18.5 KB | 0.7% |
5.92 |
| .xdata | 0x281c00 | 34.0 KB | 1.3% |
5.48 |
| .idata | 0x28a400 | 10.5 KB | 0.4% |
4.56 |
| .CRT | 0x28ce00 | 512 B | 0.0% |
0.39 |
| .tls | 0x28d000 | 512 B | 0.0% |
0.0 |
| .reloc | 0x28d200 | 4.0 KB | 0.2% |
5.32 |
| Import table (inside a section) | 0x28a400 | 10.2 KB | 0.4% |
Byte map
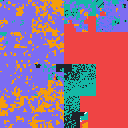
The whole file as a 128×128 picture: each pixel is 163.53 bytes, laid along a Hilbert curve so that bytes close in the file stay close in the picture and each part shows as a block. Starts top-left, ends top-right.
- Compressed / encrypted 29.2%
- Dense data 14.4%
- Code / structured data 40.7%
- Low entropy (headers, tables) 10.5%
- Text / strings 1.0%
- 0x00 padding 4.2%
Windows executable
Exploit mitigations · set by the linker; hand-built malware often ships without them
Packers, installers and compilers identified (1)
| Name | Kind | Evidence |
|---|---|---|
| MinGW (GCC) | compiler | string Mingw-w64 runtime failure |
Capabilities from imports and Rust crates
| Capability | APIs / types | ATT&CK |
|---|---|---|
| Encryption (CryptoAPI / CNG) | BCryptGenRandom | T1486 |
| File enumeration | FindFirstFileAFindFirstFileExWFindFirstFileWFindNextFileAFindNextFileWGetDriveTypeWGetLogicalDrives | T1083 |
| Network share enumeration | NetServerEnumNetShareEnumWNetEnumResourceWWNetOpenEnumW | T1135 |
| Service control | ControlServiceOpenSCManagerA | T1489 |
| Process enumeration / termination | CreateToolhelp32SnapshotProcess32FirstWProcess32NextWTerminateProcess | T1057T1489 |
| Anti-debugging | CheckRemoteDebuggerPresentIsDebuggerPresent | T1622 |
| Wallpaper change | SystemParametersInfoW | T1491.001 |
| Token / privilege manipulation | AdjustTokenPrivilegesLookupPrivilegeValueWOpenProcessToken | T1134 |
| Encryption (crypto library) | cipher | T1486 |
Sections
| Name | Virtual address | Virtual size | Raw size | Flags | Entropy | Notes |
|---|---|---|---|---|---|---|
| .text | 0x1000 | 1,283,400 | 1,283,584 | R-X |
6.35
|
entry point |
| .data | 0x13b000 | 2,864 | 3,072 | RW- |
0.298
|
|
| .rdata | 0x13c000 | 1,321,856 | 1,321,984 | R-- |
6.948
|
|
| .pdata | 0x27f000 | 18,480 | 18,944 | R-- |
5.916
|
|
| .xdata | 0x284000 | 34,600 | 34,816 | R-- |
5.476
|
|
| .bss | 0x28d000 | 9,312 | 0 | RW- |
0.0
|
empty on disk |
| .idata | 0x290000 | 10,444 | 10,752 | RW- |
4.557
|
|
| .CRT | 0x293000 | 104 | 512 | RW- |
0.389
|
|
| .tls | 0x294000 | 16 | 512 | RW- |
0.0
|
|
| .reloc | 0x295000 | 3,884 | 4,096 | R-- |
5.319
|
Imports (240)
Rust crates (29)
Libraries the program was built with, from the Cargo paths left in it.
Cryptographic constants 4
Tables and constants of the algorithms compiled into the file, recognised without running or decrypting anything. A locker that brings its own cipher (ChaCha20, AES, Curve25519) needs no CryptoAPI import; many legitimate programs carry the same libraries, so this is context, not a verdict.
| Algorithm | Kind | Evidence | Confidence | Hits | First at |
|---|---|---|---|---|---|
| ChaCha20 / Salsa20 | stream cipher | "expand 32-byte k" | high | 8 | 0x13d710 |
| ChaCha20 / Salsa20 | stream cipher | sigma as code immediates | high | 8 | 0x13d710 |
| SHA-256 | hash | K constants | high | 1 | 0x13d930 |
| SHA-256 | hash | initial values | medium | 1 | 0x2430d8 |
| CRC32 | checksum | table | high | 1 | 0x248200 |
| SipHash | hash | initialization constants | high | 10 | 0x64af7 |
Indicators extracted from strings · from 2,936 strings. Only those listed under Known indicators are in our database
IOC matches are re-checked against the database every time this page loads. YARA and static analysis ran once, when the file was first analysed (analyzer v6).